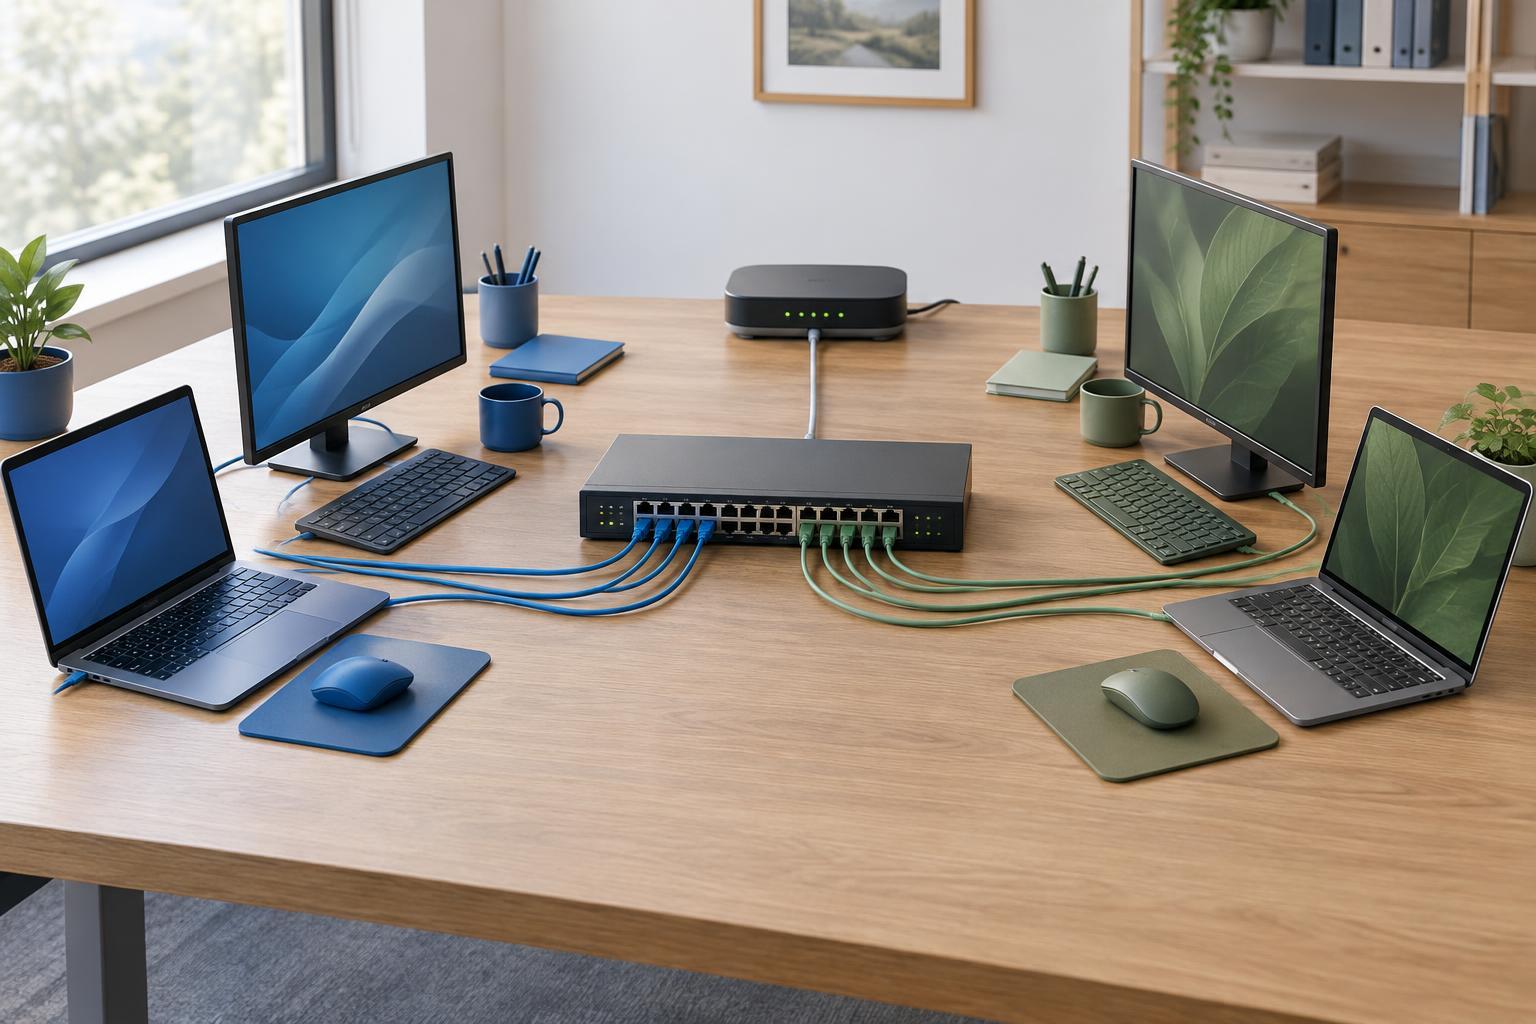
What a VLAN separates
A virtual local area network, or VLAN, is a way to create separate logical networks using shared switching equipment. Imagine a small office with employee computers, guest Wi-Fi and printers connected through the same set of switches. Without deliberate separation, many of those devices could occupy one large local network. VLANs let an administrator group connections by purpose rather than by which switch or room they use.
Each VLAN forms its own Layer 2 broadcast domain. A broadcast sent by a device in one VLAN is normally delivered only to ports in that VLAN, even when the switches carrying those VLANs are physically connected. A device on VLAN 10 does not communicate directly at Layer 2 with a device on VLAN 20. That distinction makes VLANs useful for organizing traffic and limiting where local broadcasts go.
A VLAN is not a separate cable, and a VLAN ID is not an IP address. The ID tells compatible network equipment which logical network a frame belongs to. In practice, administrators often assign a different IP subnet to each VLAN so that addressing and routing follow the same boundaries.
Access ports and trunk links
A switch port connected to an ordinary endpoint, such as a desktop computer, is commonly configured as an access port. It belongs to one VLAN, and the endpoint typically sends and receives Ethernet frames without VLAN tags. The switch associates incoming traffic on that port with its configured VLAN.
A link between switches may need to carry several VLANs at once. Such a link is commonly configured as a trunk. With IEEE 802.1Q tagging, the switch adds information to Ethernet frames that identifies their VLAN, allowing the receiving switch to keep the traffic separated. Only VLANs configured to cross that trunk can use it; a VLAN does not automatically become available everywhere merely because it exists on one switch.
Trunks can also have a native VLAN whose frames may be sent without a tag, depending on the configuration. Mismatched native VLAN settings can lead to confusing connectivity and unintended traffic placement. For a small network, recording which ports are access ports, which are trunks and which VLANs each trunk carries can prevent many avoidable mistakes.
How devices on different VLANs communicate
Separation does not mean communication is impossible. If an employee computer needs to reach a printer on another VLAN, traffic must pass through a device that routes between the VLANs. That device might be a router, a firewall or a Layer 3 switch. Each VLAN typically has a gateway address in its own IP subnet, and devices send traffic for other subnets to that gateway.
Routing also creates a useful place to apply policy. For example, a team might allow employee devices to reach a printer VLAN while preventing guest devices from reaching it. The precise controls depend on the router or firewall configuration. A VLAN alone provides Layer 2 separation; it does not, by itself, define who is allowed to communicate once routing is enabled.
A small-office example
Suppose an office assigns VLAN 10 to employee devices, VLAN 20 to guest Wi-Fi and VLAN 30 to printers. Employee desk ports are configured as access ports in VLAN 10. Printer ports are access ports in VLAN 30. The guest wireless network is mapped to VLAN 20 by the wireless equipment. A trunk between the switch and that equipment carries the VLANs the equipment needs.
The office then gives each VLAN its own IP subnet and gateway. A firewall routes traffic between subnets and applies the intended rules: guests can reach the internet but not office printers; employees can reach the printers. This example separates traffic by function while reusing switches and cabling. It also shows why VLAN setup and firewall rules need to be planned together.
Plan the boundary, then test it
Start with a simple list of device groups and the connections each group actually needs. Assign VLAN IDs and IP subnets consistently, label switch ports, and limit trunks to the VLANs they must carry. Check that the router or firewall has the appropriate gateway interface for every VLAN that needs routed access.
After configuration, test from a device in each group. Confirm that it receives an address from the intended subnet, can reach its gateway and can access only the destinations you meant to allow. If a device cannot connect, check its access-port assignment, the VLANs allowed on intervening trunks, IP addressing and routing rules. VLANs are most useful when the logical design is documented and the observed traffic matches it.


