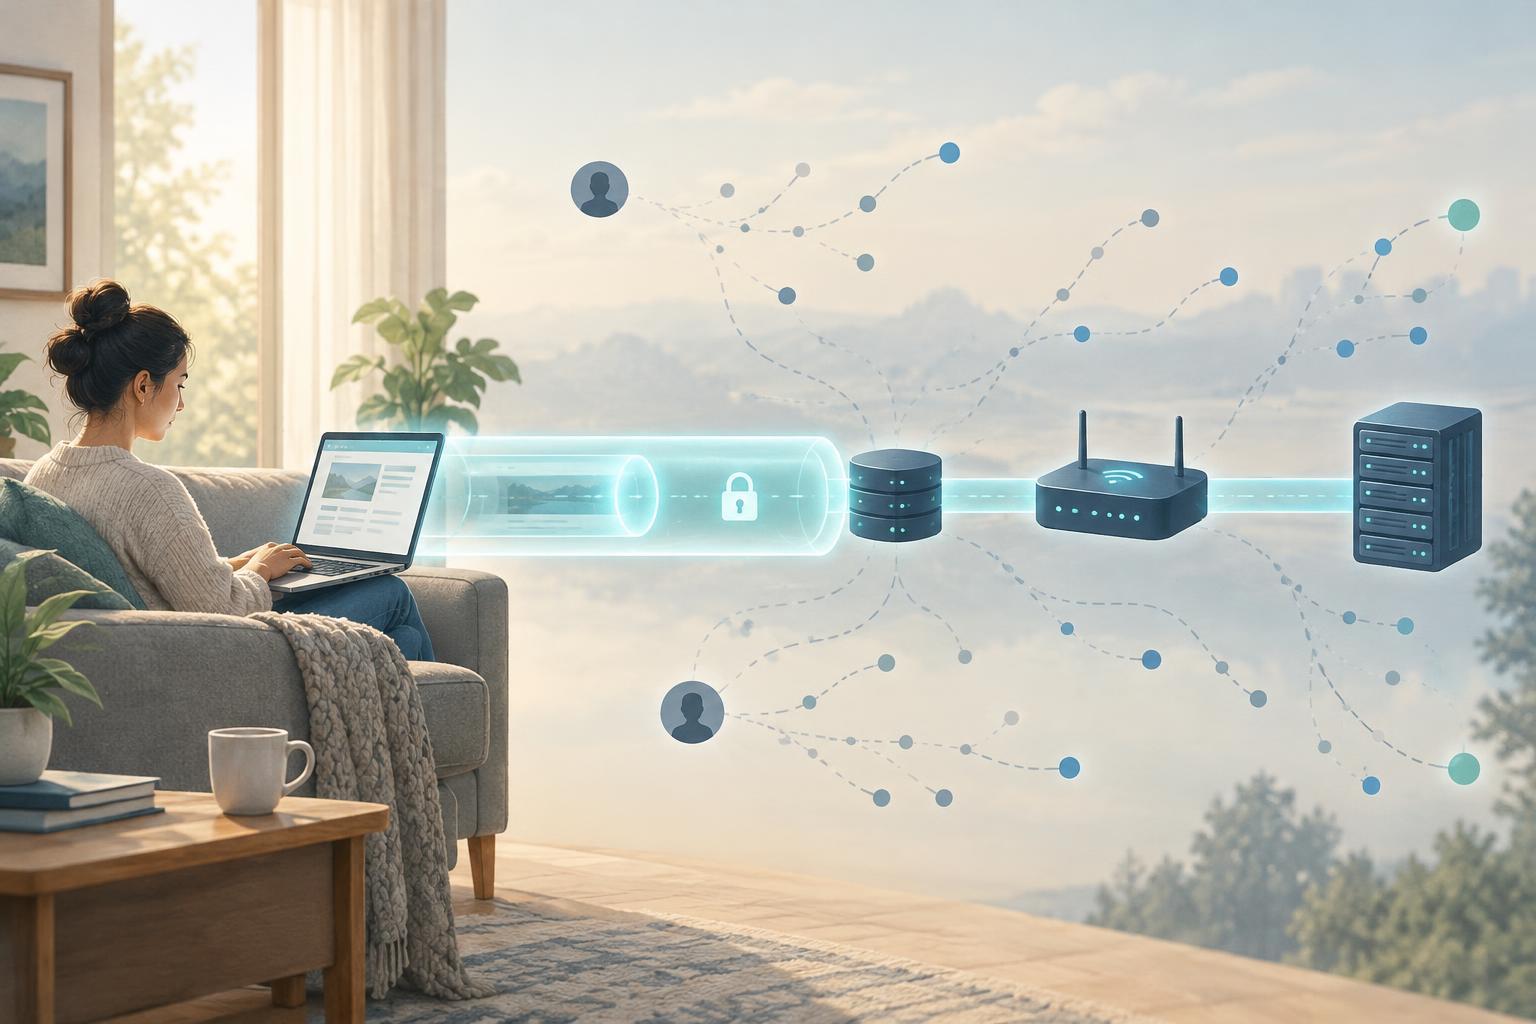
A website visit leaves more than one kind of clue
When you open a website, your device may first look up its domain name using DNS, then connect to a server address and establish an HTTPS connection. Those steps expose different information to different parties. The key distinction is between the contents of a visit—such as a page’s text and the data you enter—and the metadata needed to route the connection.
A useful way to picture this is as a sequence: domain lookup, network connection, encrypted page request. Privacy depends on who can observe each step and which protections are in use. No single setting makes a visit invisible to everyone.
What HTTPS hides—and what it usually does not
HTTPS encrypts the exchange between your browser and the website after a secure connection is established. Someone watching the network generally cannot read the page you request, its URL path or query string, the form data you send, or the response you receive. They can usually tell that your device connected to a particular IP address, when it connected and roughly how much data moved.
The destination IP address is not always a reliable name for the site. Many websites share hosting infrastructure or content delivery networks, so one address may serve several domains. Other clues can narrow the possibilities. In many HTTPS connections, the browser sends a hostname in a field called Server Name Indication, or SNI, that a network observer can read. Encrypted Client Hello (ECH) can protect that hostname, but only when the browser, site and supporting infrastructure use it; it should not be assumed to be active.
HTTPS also does not hide a visit from the website itself. The site receives your requests and may recognize you through a login, cookies or other information you provide. On a device managed by an employer or school, installed monitoring software—or a configured inspection proxy with a trusted certificate—may provide additional visibility beyond what an ordinary network observer has.
Why DNS matters for privacy
DNS translates a name such as example.com into an address your device can connect to. With traditional, unencrypted DNS, an observer on the path to the DNS resolver may be able to see the names your device asks about. The resolver also receives those queries. A lookup is a clue, not proof that you read a particular page: software can request names in the background, and cached answers can let a visit proceed without a new lookup.
Encrypted DNS, commonly delivered as DNS over HTTPS (DoH) or DNS over TLS (DoT), protects queries between your device and the chosen resolver from observers along that part of the route. It does not hide the queries from the resolver. Nor does it conceal the IP addresses your device later contacts or automatically protect an exposed SNI hostname. Browser and operating-system settings can differ, so the resolver handling one application’s queries may not handle every application’s queries.
Who can see what?
A person who runs your local Wi-Fi network, or your internet provider, can generally observe the connections leaving your network. Without encrypted DNS, they may also see DNS queries. With encrypted DNS, they may see that you are contacting a resolver instead, while destination IP addresses and any unprotected connection metadata remain visible. If you share a home connection, its owner does not automatically gain access to the contents of your HTTPS pages.
A DNS resolver can see the names sent to it and information about where the queries came from, though the details depend on how your network is configured. A website you visit can see requests made to it and the information needed to deliver a response. Other services embedded in a page may receive separate requests from your browser. That is a different issue from whether someone on the network can read your HTTPS traffic.
A VPN changes the path of your traffic. Your local network and internet provider generally see a connection to the VPN rather than direct connections to each destination. The VPN provider becomes a party that can observe destination-related metadata, however, and it may handle DNS queries too. HTTPS still protects page contents from a VPN provider that is not inspecting your device or acting as a trusted HTTPS intermediary. A VPN shifts trust; it does not eliminate it.
Choose protections for the problem you want to solve
Use HTTPS sites and pay attention to browser certificate warnings: HTTPS is the main protection against someone on the network reading or changing page content in transit. If you want to reduce who can read DNS queries along the network path, check whether your browser or device uses encrypted DNS and which resolver it trusts. If you use a VPN, understand that its provider takes on visibility previously held by parts of your network path.
Finally, separate network privacy from privacy on your device and at the website. Private browsing can limit history stored by your browser after a session, but it does not make your network activity invisible. Logging into a site makes you identifiable to that site regardless of encrypted DNS. Asking “who am I trying to hide this from, and what can they observe?” is more useful than looking for one setting that promises complete anonymity.


