What cloud IAM controls
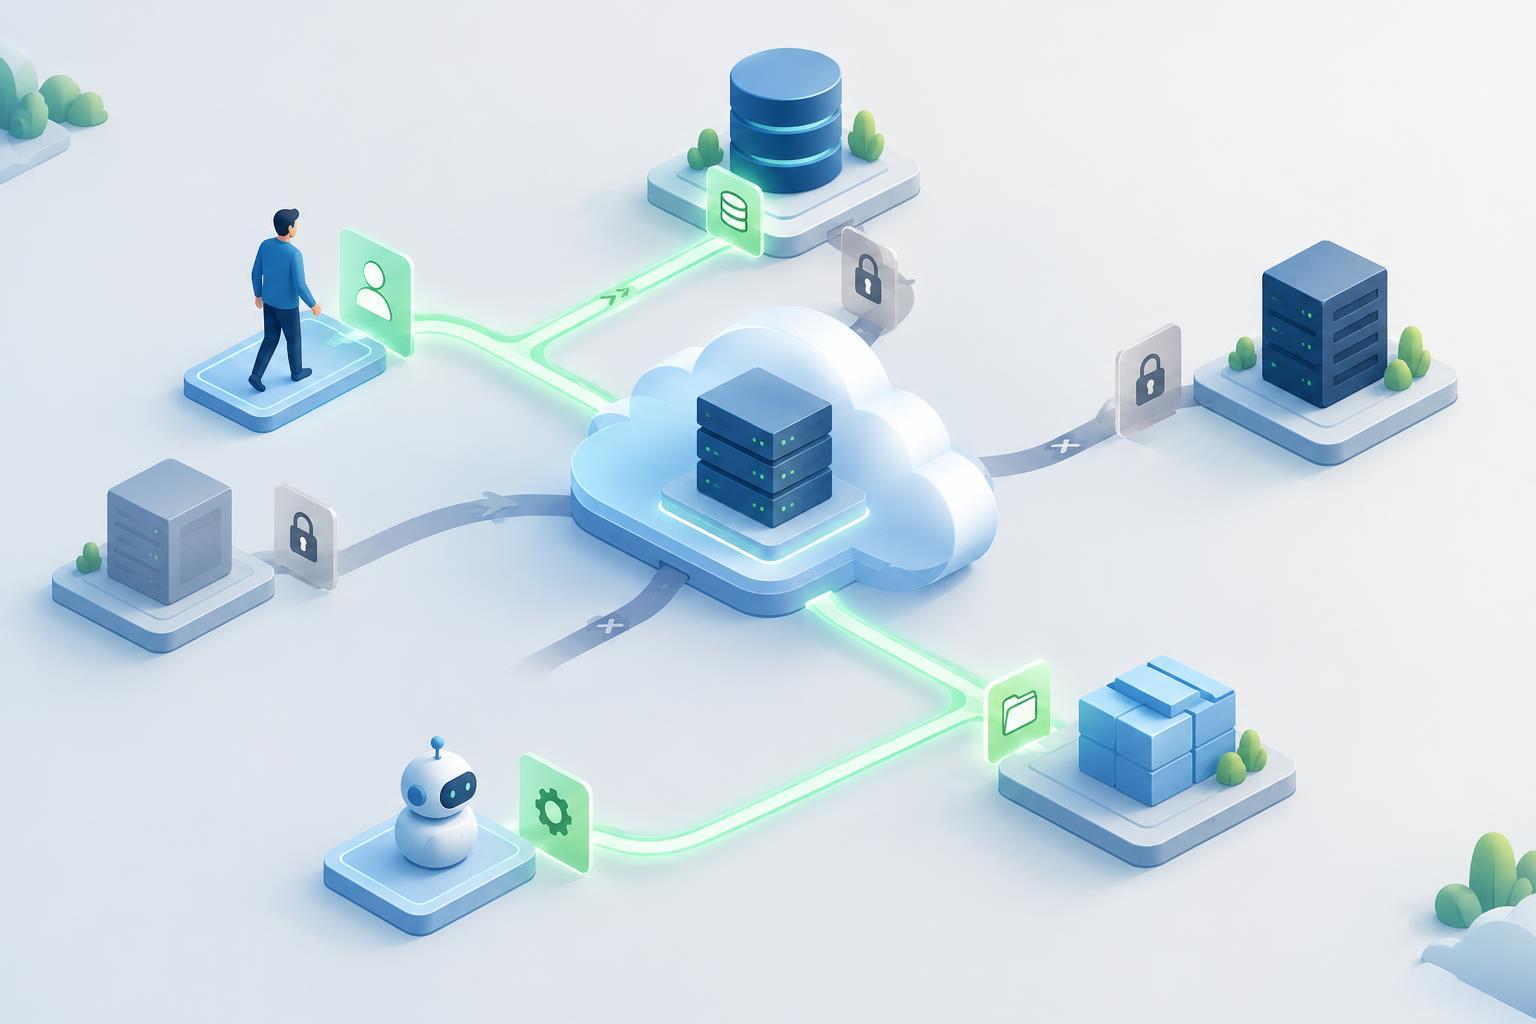
Identity and access management, or IAM, is the system a cloud platform uses to decide whether an action is allowed. When someone tries to view a storage object or a service tries to write a log, IAM helps answer three questions: Who is making the request? What action are they requesting? Which resource are they trying to use? The answer may also depend on conditions such as the account, project or environment involved.
IAM is not the same as keeping data private by default. A permission to read an object, a resource setting that permits sharing, and an application’s own login rules can all affect access. Cloud providers organize these controls differently, so learn your platform’s terminology and check the effective access rather than assuming that one policy tells the whole story.
Users, service identities and roles
A user identity usually represents a person who needs to sign in and perform work. A service identity represents software, such as a web application or scheduled job. Keeping these identities separate makes activity easier to understand and lets you remove one person’s or workload’s access without disrupting others. Avoid sharing a single identity across a team: shared access makes it harder to determine who changed a setting.
A role is a way to bundle permissions for a job or workload. For example, an application that displays files might need permission to read objects in one storage location, but not to delete them or create new users. Depending on the provider, a role may be a named collection of permissions, an identity that can be assumed temporarily, or both. Policies or assignments connect those permissions to identities and resources.
Prefer temporary credentials for workloads when the platform supports them. A workload can obtain access through an assigned identity or role instead of storing a long-lived secret in code or a configuration file. Human users should have their own sign-ins and use multifactor authentication where available, especially for accounts with broad administrative access.
Least privilege in a practical example
Least privilege means granting only the actions, resources and duration needed for a task. Suppose a reporting job reads sales data from one storage location each night and writes a summary to another. It needs read access to the input and write access to the output. It does not need permission to delete either location, manage billing or change other identities’ access.
Start by listing the job’s actual operations. Identify the input and output resources, then create a role or policy scoped to those resources. Where the platform allows it, narrow the permitted actions to reading the input and writing the output. Assign that access to the job’s service identity, run the job, and investigate any denied requests. Add a permission only after confirming why it is needed.
Scope matters as much as the action. A read permission across every storage location is broader than a read permission on one location. Likewise, a deployment tool that needs powerful access during a release may not need it continuously. Some platforms offer time-limited elevation or approval workflows for such tasks.
Common access mistakes
Broad administrator roles are convenient when setting up a project, but they can hide which permissions a workload actually needs. Using them as a permanent fix for an access error makes later changes riskier. Another common mistake is copying a policy from a different environment without checking its resource scope. A policy intended for a test project may be inappropriate for production.
Secrets deserve separate attention. Even a carefully scoped identity can be misused if its credentials are exposed. Do not place access keys in source code, shared documents or application logs. If a static credential is unavoidable, limit its permissions, store it using an appropriate secret-management mechanism and have a plan to replace it. Removing a user from a team does not necessarily revoke credentials that were created separately; check those too.
A repeatable way to review access
Make access review part of routine maintenance. For each user and service identity, ask what task it supports, which roles it has, what resources those roles reach, and whether the identity is still used. Pay particular attention to administrator access, permissions that can grant further access, and identities with long-lived credentials. Remove access that no longer has a clear purpose.
Before changing a policy, test it against the intended task and a few actions that should be denied. Use the platform’s policy-testing and activity-log features where available, while remembering that logs may not capture every possible future action. Document why an exception exists and who owns it. The aim is not to write the shortest policy; it is to make access specific enough to understand, test and maintain.


