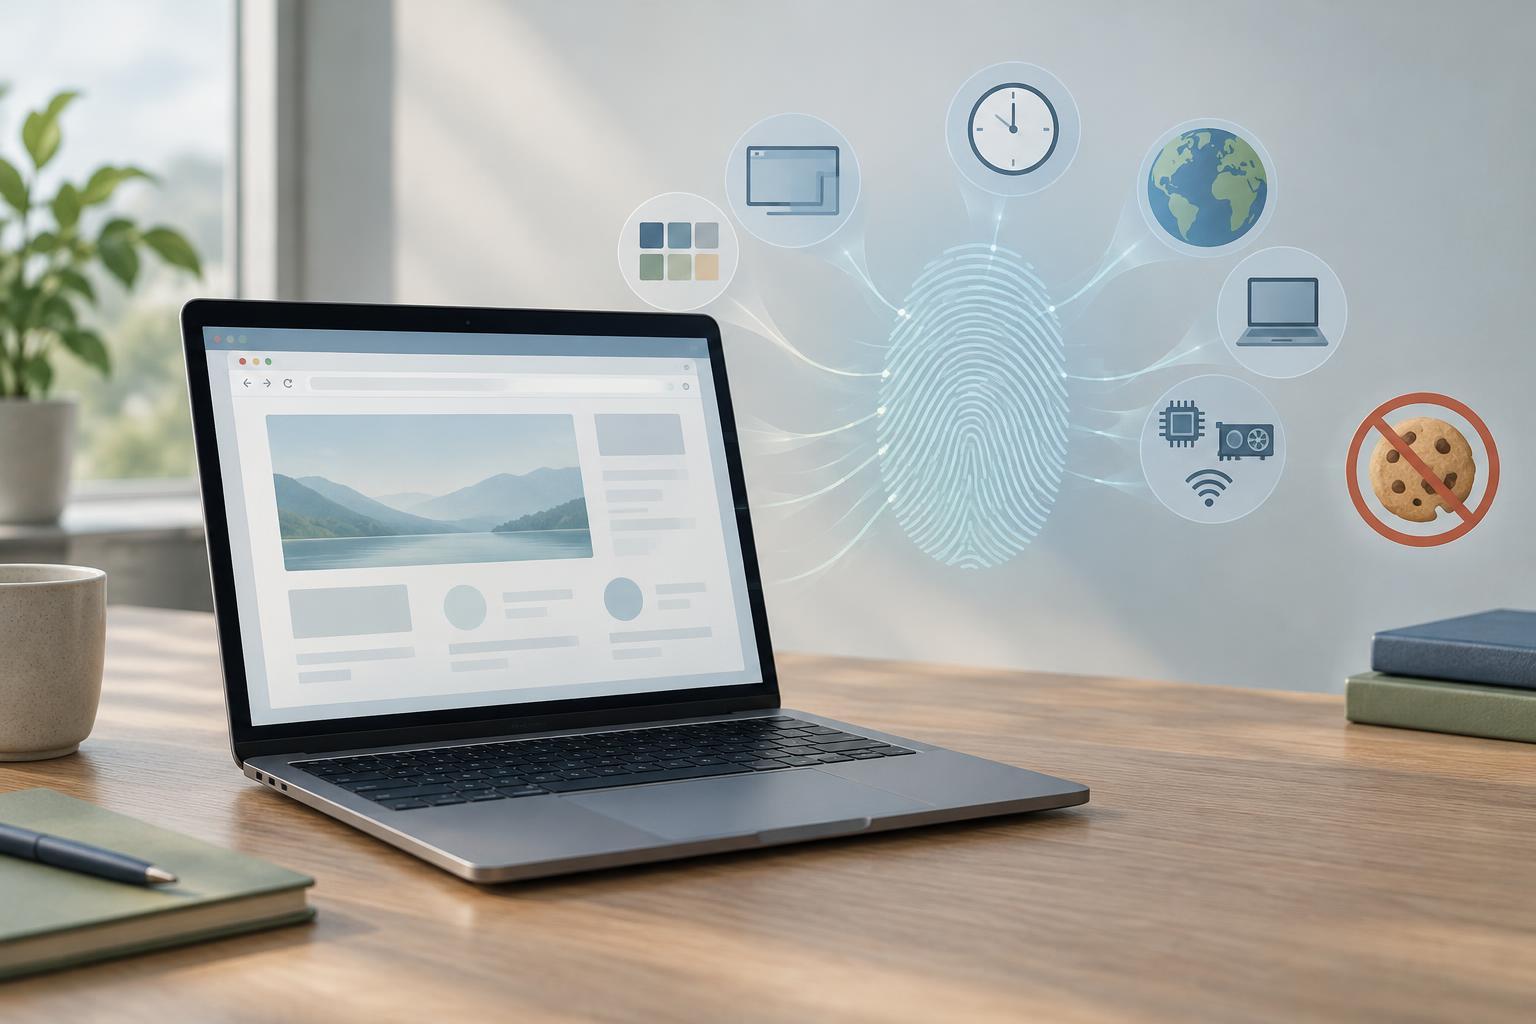
A fingerprint is a combination of clues
A cookie is a small value a website can ask your browser to store and send back on later visits. Browser fingerprinting takes a different approach: a site or an embedded script observes characteristics of the browser and device, then combines them into a profile. On a return visit, it compares the new profile with earlier ones. If they are similar enough, the operator may infer that the visits came from the same browser.
Possible clues include browser and operating-system details, language preferences, time zone, screen dimensions, supported features and how the browser renders certain graphics. A web server can observe some information in a request, while a page script can test additional capabilities after the page loads. An IP address can also help link visits, but it is a network identifier rather than a browser fingerprint component that stays fixed to one browser.
No single clue has to be unique. Many people share a screen size or language setting. The tracking value comes from combining clues that are less common together. Even then, a fingerprint is not a permanent device serial number: software updates, changed settings and network conditions can alter the observations.
How a site builds and compares one
Imagine two visitors using the same browser version. Both report similar basic browser information, but one has a different time zone, screen size and set of available fonts. A fingerprinting script can collect these differences through browser interfaces and turn the results into a compact identifier or a set of values for comparison. The identifier is usually created by the tracker; the browser does not hand out a universal fingerprint number.
Some tests ask the browser to perform a task and inspect the result. For example, drawing text or graphics to a canvas can produce slightly different output across combinations of software, fonts and graphics hardware. Other tests look at supported APIs or audio-processing results. A tracker may use only a subset of these signals, because collecting more information can be slow, noticeable or restricted by the browser.
When the browser returns, the tracker may compare the new observations with stored records. An exact match is simple to recognize; a partial match requires a judgment about how much change to allow. That creates a trade-off: strict matching misses returning visitors whose setup changed, while loose matching risks grouping different people together.
Why blocking cookies is not the whole answer
Deleting cookies removes stored identifiers, but it does not necessarily change the characteristics a page can observe. Similarly, private browsing generally limits what is retained locally between sessions; it does not guarantee that every visit looks unrelated to a site. Fingerprinting is useful to trackers precisely because it can work without placing a persistent identifier in browser storage.
Recognition across websites requires a way to bring observations together. For example, the same third-party service might receive data when its code runs on multiple sites. Browser restrictions on third-party resources can limit some of these opportunities. Fingerprinting alone does not reveal a person's name, and its accuracy depends on how distinctive and stable the available signals are. If someone also signs in to an account, however, a service may be able to associate observed visits with that account.
Practical ways to reduce fingerprinting
Start with a browser that includes tracking protections, and keep it updated. Some browsers limit access to fingerprinting signals, make certain results less precise, or block known tracking scripts. Review privacy settings rather than assuming that a cookie toggle covers every tracking method. Blocking third-party trackers can also reduce how often the same service observes you across unrelated sites.
Avoid making your browser unnecessarily distinctive. Installing many unusual extensions or changing numerous low-level settings may create a rarer combination of characteristics, even if each change seems privacy-friendly on its own. Extensions that block requests can be useful, but a large collection may cause site breakage without providing a clear extra benefit. If you need stronger separation between activities, consider using separate browser profiles or browsers; this limits shared storage and some shared context, though it does not guarantee that the profiles cannot be linked.
Be cautious of any tool promising complete anonymity from fingerprinting. Protections differ by browser, website and threat model. A more realistic goal is to expose fewer signals and reduce the number of parties that can collect them, while accepting that websites still need some information to display pages and handle requests.
The key distinction
Cookies recognize a browser by asking it to return a stored value. Fingerprinting tries to recognize it from observable characteristics. Both can support legitimate functions, such as detecting unusual account activity, as well as unwanted tracking. Understanding that distinction helps explain why clearing cookies is useful but incomplete: it removes one route to recognition, not every clue a browser can reveal.


